$ loading...
ZeroDay Cyber Feed
Explore fresh threat intelligence, zero-day vulnerabilities, and cyber news. Stay ahead of the curve with our real-time feed of the latest in cybersecurity.
Help keep ZeroDay free for everyone. Donate any amount (Donante) to support independent cybersecurity education and daily threat intelligence updates.
Professional Course Tracks
Learn offensive security, network exploitation, red team operations, and real-world penetration testing techniques aligned with industry standards and hands-on vulnerability assessment practices.
Most detailed category with step-by-step breakdowns, realistic scenarios, and practical examples.
CVE posts are concise vulnerability summaries for fast awareness and prioritization.
Infrastructure assessment, exposure mapping, and internal attack-chain coverage for practical testing.
Follow CVE summaries for context, then move to Red-Team for deeper techniques and examples.

A sophisticated supply chain attack is exploiting compromised npm packages to steal developer credentials and propagate itself across the open-source ecosystem, posing a significant risk to software development pipelines

A sophisticated threat actor known as Harvester has updated its arsenal with a new Linux variant of its GoGra backdoor, employing legitimate cloud services for command and control to evade detection. This development sig

A severe security flaw in Cohere AI's Terrarium sandbox could allow attackers to execute arbitrary code with root privileges, posing a significant risk to systems running untrusted code. The vulnerability, CVE-2026-5752,
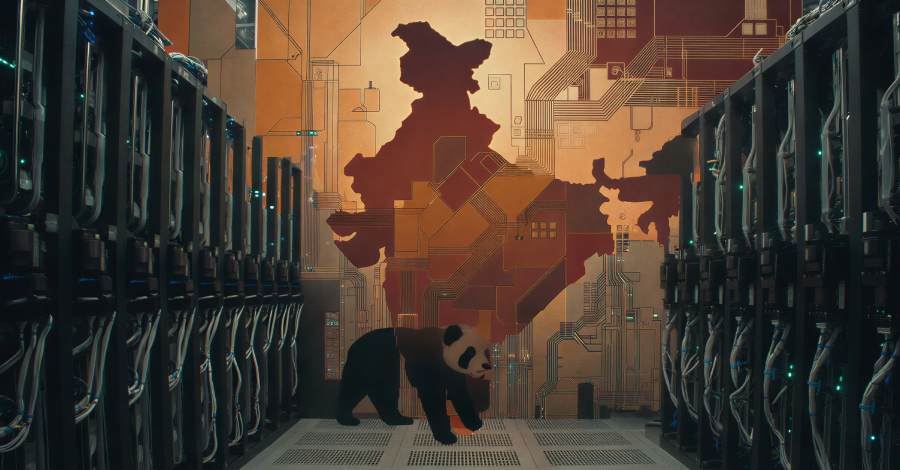
A sophisticated malware variant, LOTUSLITE, has been updated by suspected Chinese state-sponsored actors to target India's financial sector and South Korean policy circles, shifting from previous espionage campaigns. Pub